Privy by IDfy Crosses 50 Indian Enterprise Implementations
Author
Aishwarya Narsipalli
Date Published
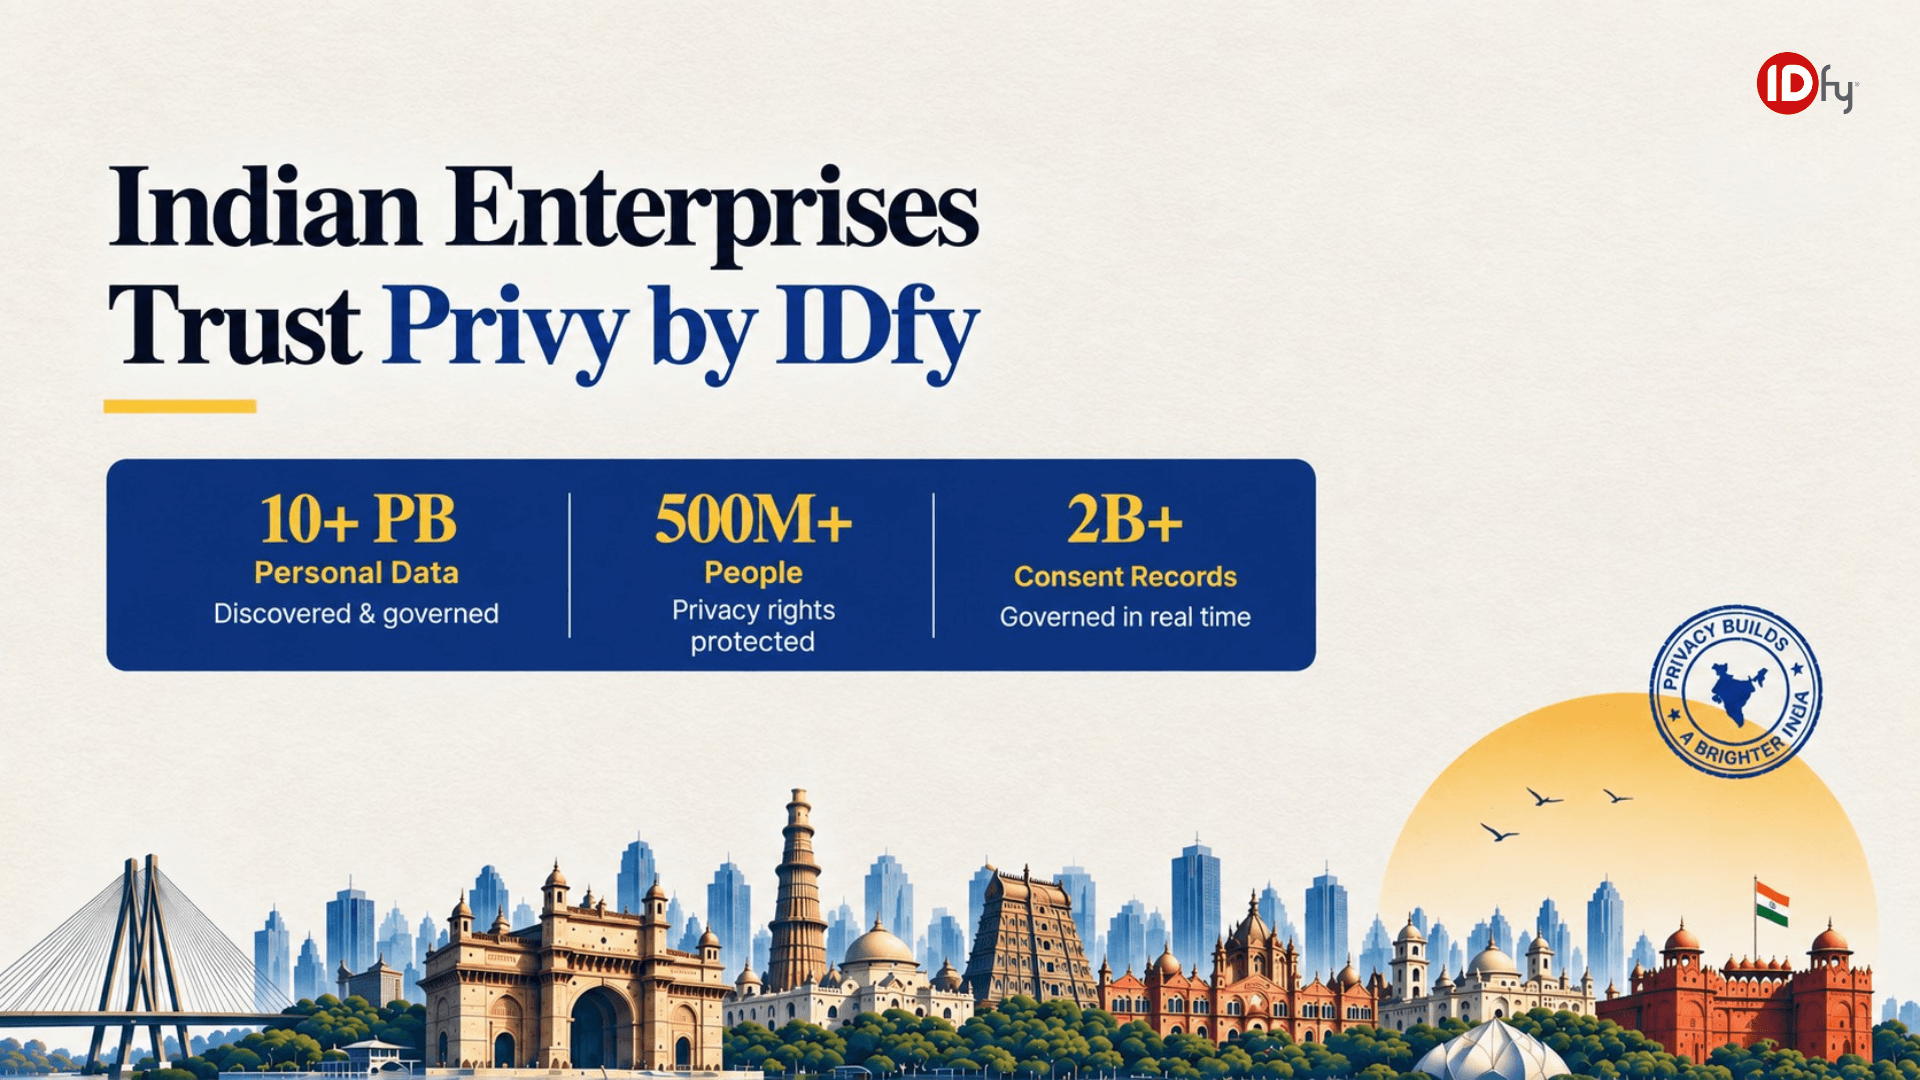
Privy by IDfy, India's leading platform for operationalizing DPDP compliance, now has more than 50 Indian enterprises implementing it. That's seven months before full enforcement of the Digital Personal Data Protection Act. The mix of enterprises says something useful about where Indian industry really stands on privacy readiness.
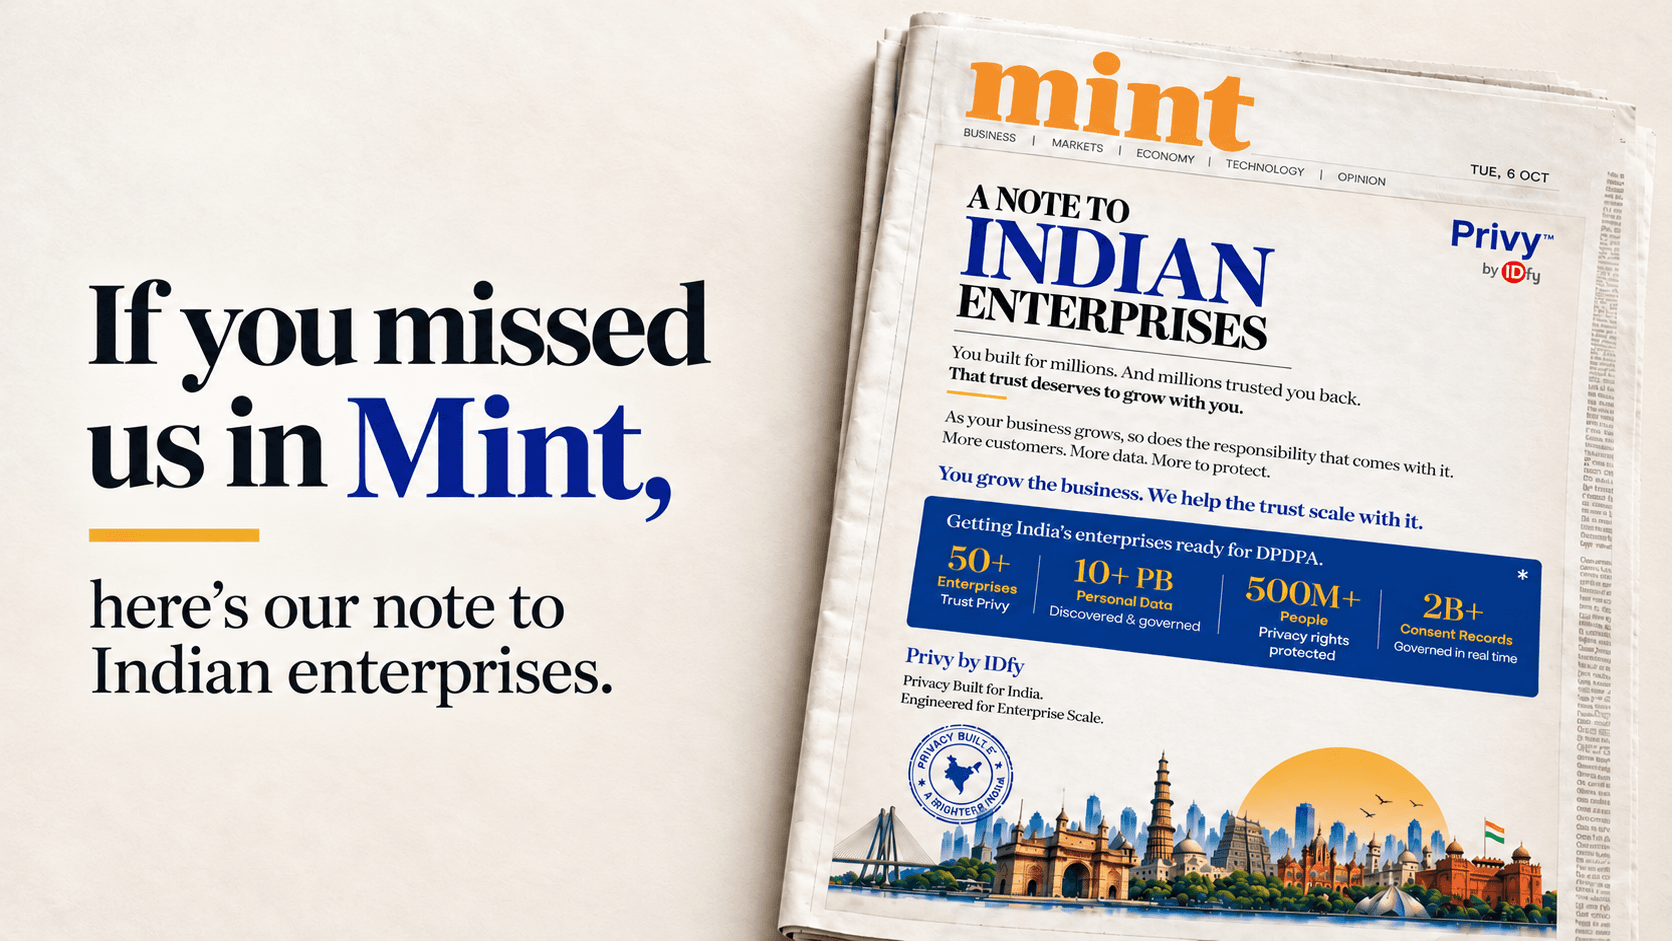
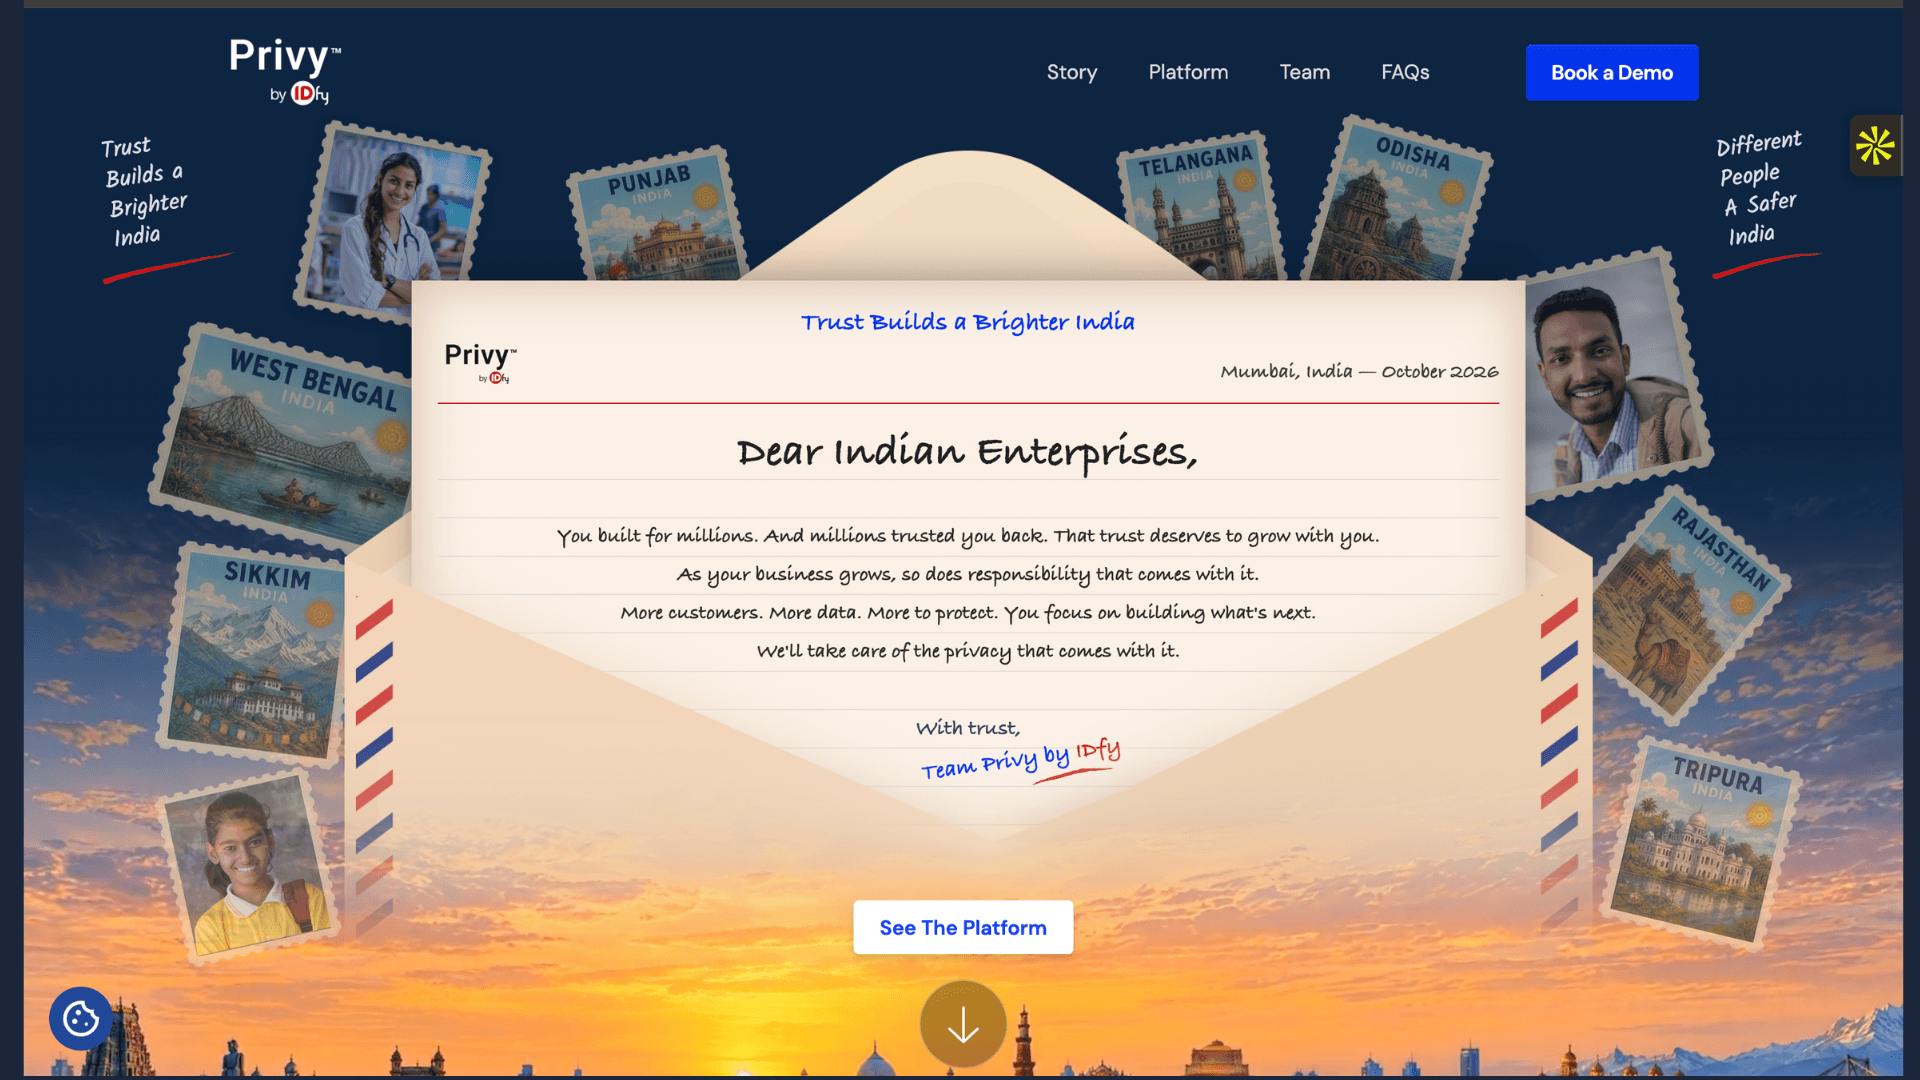
Privy was featured in Mint's Mumbai edition on 6 October 2026 with a note to Indian enterprises. The note carried the scale these implementations are built to reach.
Privy by IDfy in Numbers
50+ enterprises. 10+ petabytes. 500M+ people. 2B+ consent records. Once the ongoing implementations are fully rolled out, that's the scale Privy by IDfy will be working at.*
Figures represent projected scale upon full rollout of ongoing Privy implementations. M = million · B = billion · PB = petabytes.
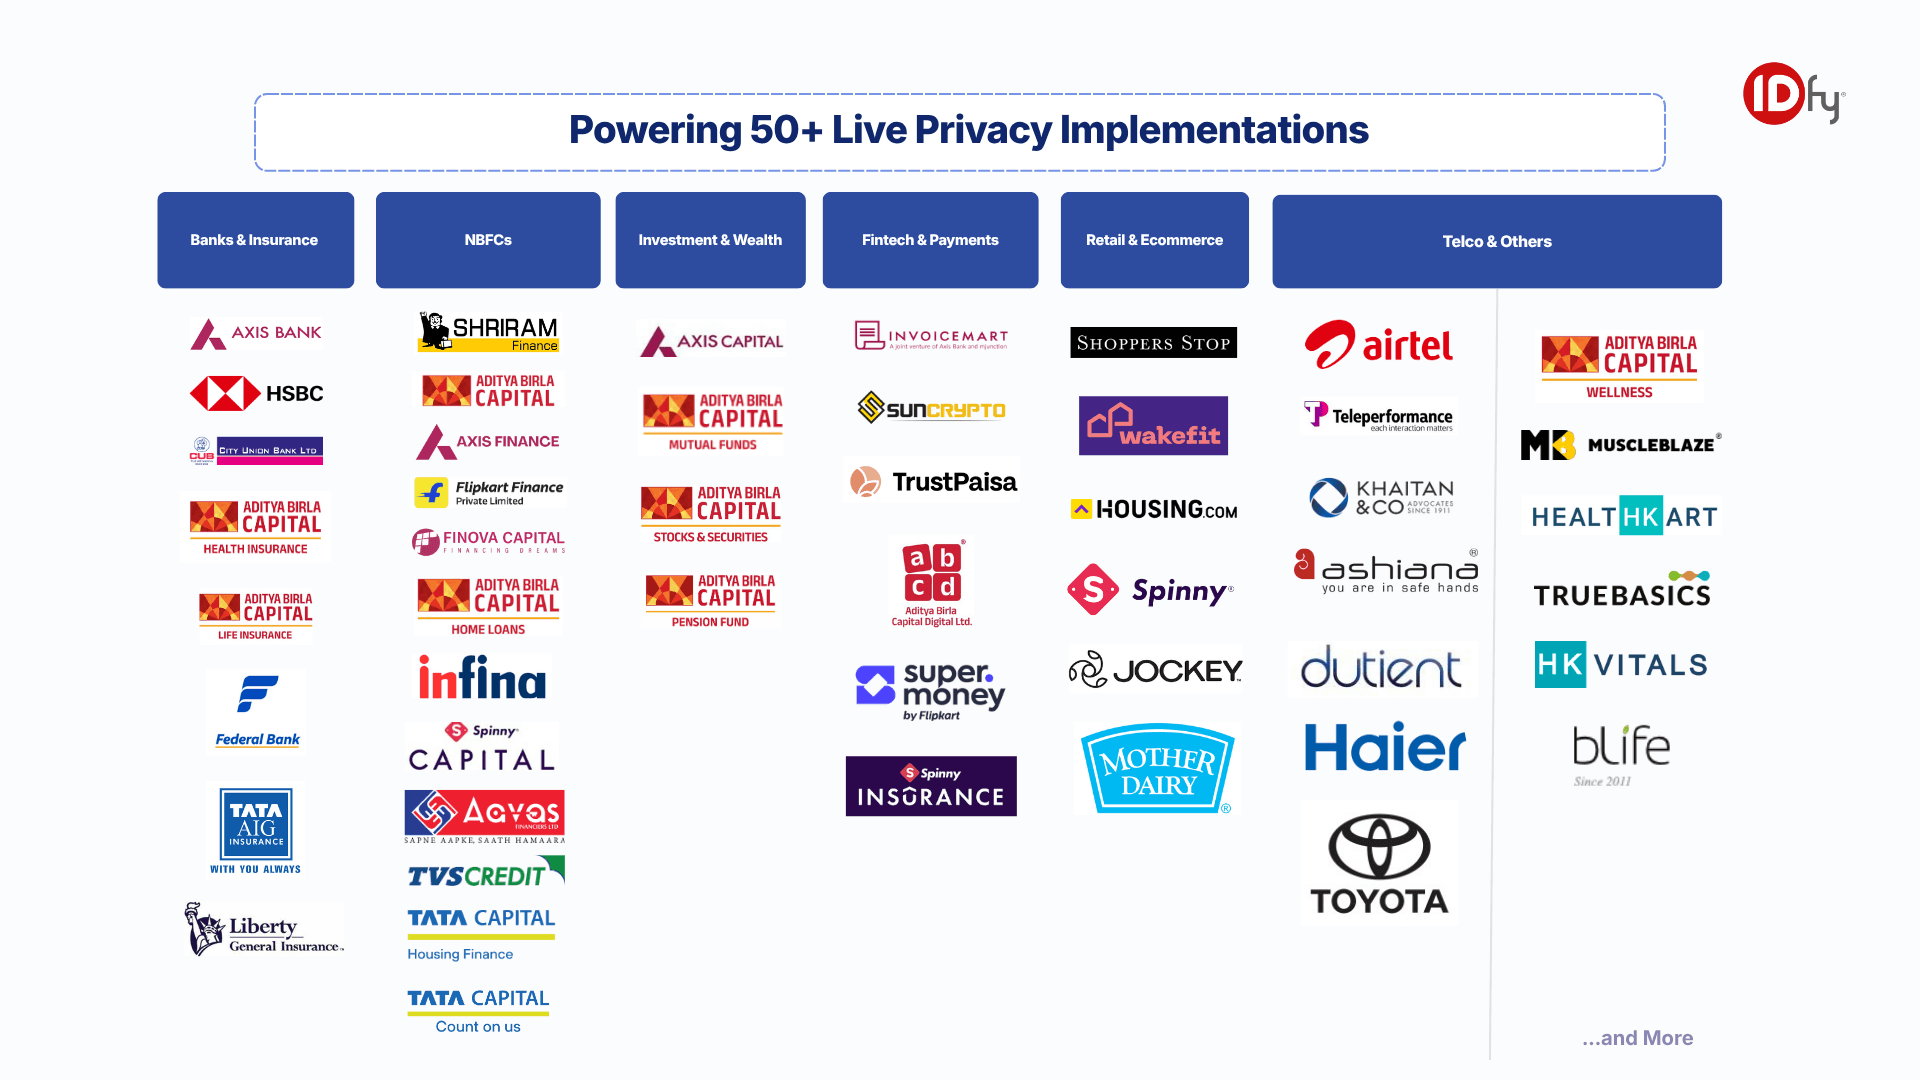
50+ enterprises. More than 50 Indian enterprises, in sectors from banking to health, have chosen Privy for their DPDPA compliance. Each one is a separate leadership team making the same call for a law that applies to all of them.
10+ PB of personal data. A petabyte is 1,000 terabytes, so that's more than 10,000 terabytes of personal data for Privy to discover and govern. It sits in CRMs, cloud storage and legacy systems that grew over years, and much of it has never been mapped end to end. At that volume, finding the data is the first job. Keeping the map current is the permanent one.
500M+ people. Every one of them is a data principal with rights under the Act. They can ask what's held about them, have it corrected or erased, withdraw consent and raise a grievance. At this scale, each of those rights has to be something an enterprise can honour on request.
2B+ consent records. Each record is an immutable, versioned consent artefact: the evidence of who agreed to what, and when. Governed in real time, 2 billion of them means 2 billion moments where an enterprise can show that consent was given. A change or a withdrawal shows up as it happens.
Four numbers, one platform. Privacy Built for India. Engineered for Enterprise Scale.
Implementations Across Industries
These implementations cover more than a dozen sectors. Banks and insurers. NBFCs and housing finance companies. Asset management, broking, capital markets and pension management. Fintech and payments. Retail, ecommerce and D2C brands. Telecom, real estate and proptech, auto marketplaces, health and wellness, business process services and professional services. Each answers to its own primary regulator, and one platform covers them all.
Some are a single company. Others are whole groups of eight or more companies. Each one is its own data fiduciary, legally responsible for the personal data it holds, and they often answer to different regulators.
We implement Privy the way your programme needs it. Want the full stack? We implement all 10 modules across the 3 pillars. Need one thing first? We implement a single module, and you add more when you're ready. Either way, it's the same platform with the same implementation support.
Built Around Where Your Data Lives
Privy by IDfy covers the full stack, and it starts from your data. Data discovery and classification, including endpoints, find where personal data sits. Auto data lineage shows how it moves. Data security posture management shows how exposed it is, and privacy-enhancing technologies protect it while it's in use.
Impact assessments, third-party risk management and incident management put controls around that data. The AI Compliance Co-pilot ties the whole stack together.
That order matters. Every obligation in the Act, from erasure to retention to purpose limitation, depends on knowing the full extent of your data. Privy is built for exactly that.
What 50+ Enterprises Have in Common
These enterprises differ in sector, size, and regulator. What they share is a position. Their customers handed over personal data because they trusted the brand. And there's a date, 13 May 2027, that doesn't move, however ready anyone feels.
They also share a choice. They started with the clock running, and they started with Privy by IDfy.
Our note in Mint put the thinking in a few short lines
You can read the full note, and what's behind it, on our page for DPDP compliance and enterprise privacy in India.
You built for millions. And millions trusted you back.
That trust deserves to grow with you.”
That is how we see these 50+ relationships. It is a partnership built around a simple idea: as businesses grow, the trust their customers place in them needs to grow with them.
The Dates That Matter
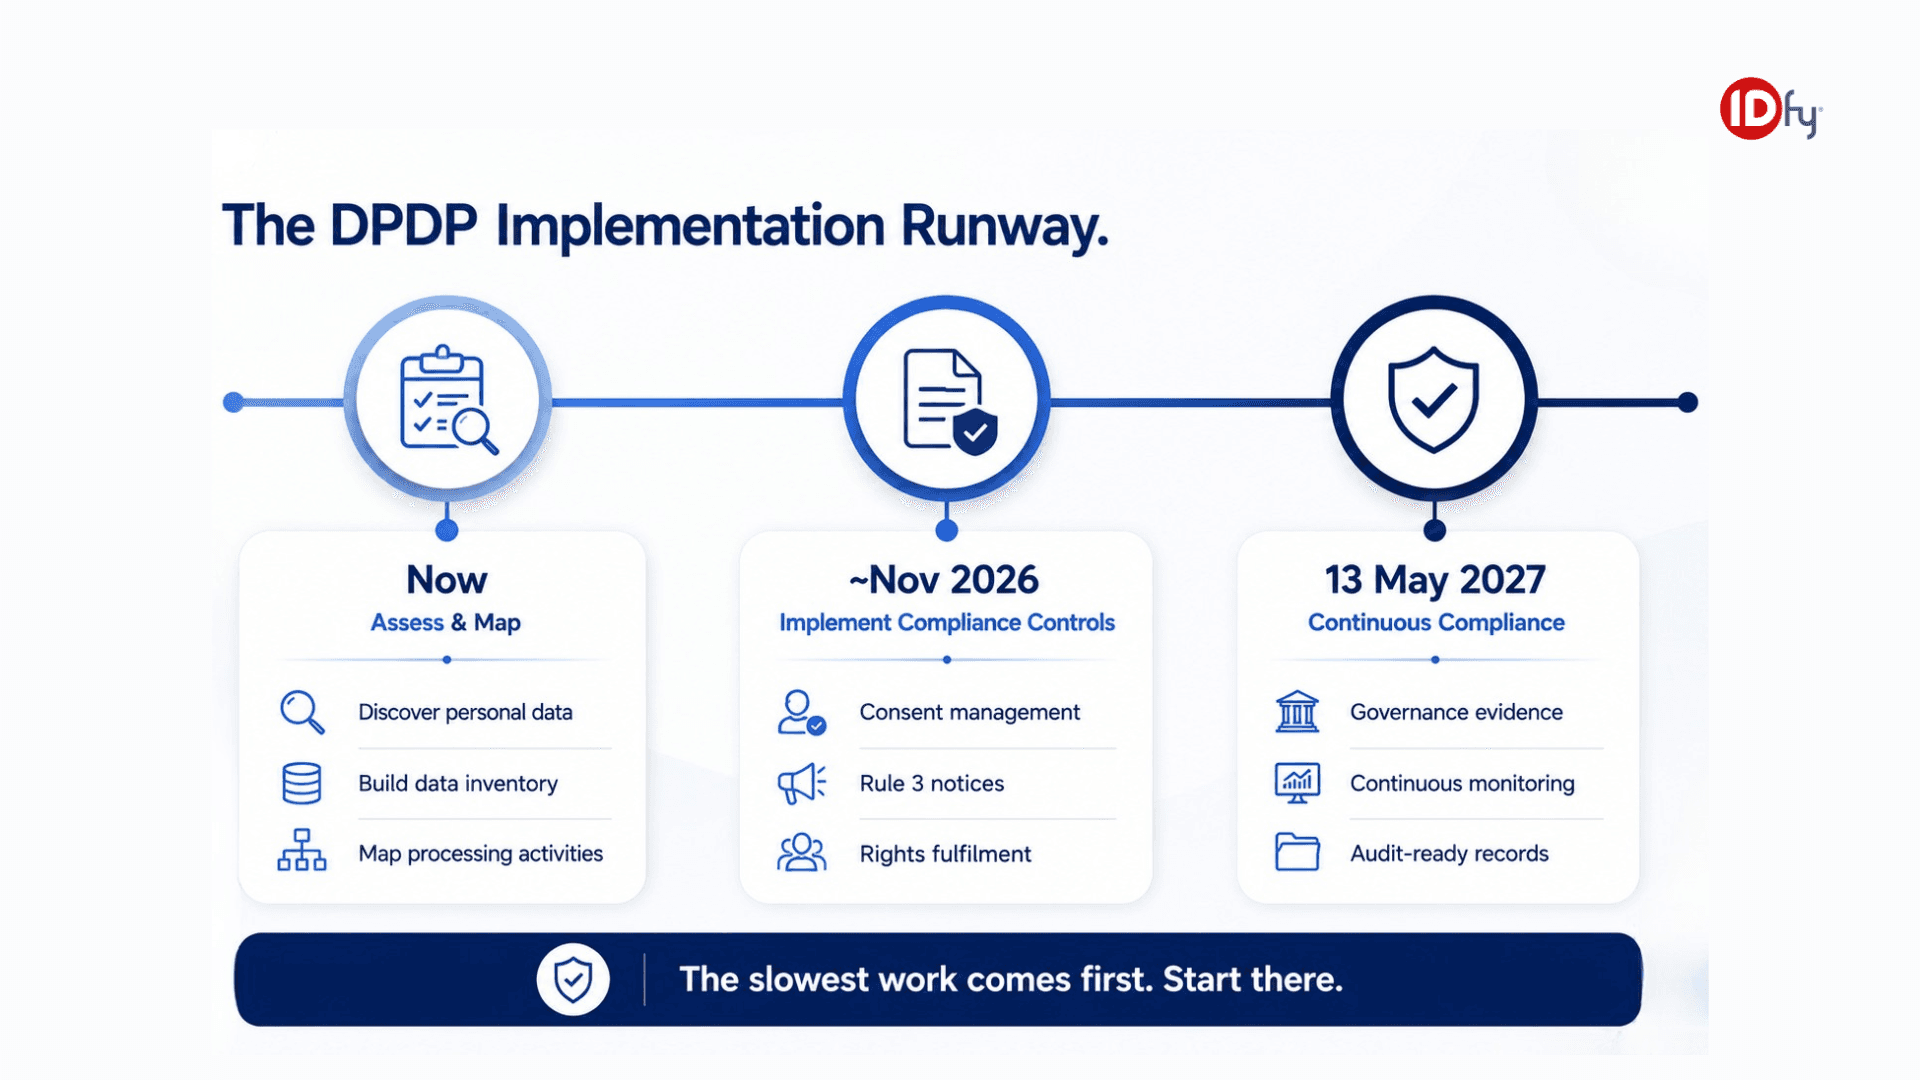
The DPDP Rules, 2025 were notified on 13 November 2025, and an 18-month phased rollout started that day. The Data Protection Board of India has been able to receive complaints since then. Consent manager registration opens on 13 November 2026. Full DPDPA compliance, covering notice, consent, security safeguards, breach reporting, and data principal rights, is due by 13 May 2027. Penalties go up to ₹250 crore per contravention.
That leaves roughly seven months, and the work runs in order. Discovery, classification, design, build. Then integration across systems that have never talked to each other, vendor and processor fixes, and a lasting change in how new data flows get approved. The DPDP compliance guide for 2026 sets out the order, and the 90-day implementation guide shows how to shorten it.
Across these 50+ implementations, the biggest predictor of delivery on schedule has been how early discovery started. Spend has mattered less.
Discovery is the place to begin, and how to map personal data for DPDP compliance shows you how.
Why Enterprises Are Choosing Privy by IDfy
IDfy has spent 15+ years handling 50+ Indian PII types across petabytes of data. Its infrastructure runs more than 60 million verifications a month. That history matters here, because almost every hard problem in DPDPA compliance comes down to identity.
Say a data principal asks what you hold about them. To answer, you need to know which records, in which systems, belong to that one person. Your core platform knows a customer ID. Marketing knows an email. The app knows a device. The contact centre knows a phone number. Match them wrongly in one direction, and you miss data you were obliged to find. Match them wrongly in the other, and you act on the wrong person's records.
Privy approaches discovery, consent and data principal requests from that identity layer.
IDfy was early, too. Its CEO, Ashok Hariharan, submitted a white paper on data privacy and consent to the Justice Srikrishna Committee in 2018.
"We have spent 15 years working with some of the most sensitive personal data in India. Five years ago, we made a deliberate long-term bet that privacy would become fundamental to the digital economy and backed that conviction with capital, people and product investment. We're proud to see that journey now entering its next phase, where privacy and trust are becoming core infrastructure for how enterprises build and grow."
Ashok Hariharan, Founder and CEO, IDfy
Privy covers 3 pillars and 10 modules, connected by an AI Compliance Co-pilot:
- Personal data discovery and governance: data discovery and classification including endpoints, auto data lineage, data security posture management, privacy-enhancing technologies.
- Continuous compliance and risk: privacy impact assessments, incident management, third-party risk management.
- Consent lifecycle management: consent governance, data principal rights management, cookie manager.
Comparing platforms? Read what a DPDPA compliance platform needs to have in 2026 and IDfy's seven things an ideal DPDP solution should have.
The product pages go deeper. Personal Data Discovery & Governance and Third-Party Risk Management cover the data and processor work.
The Consent Governance Platform and Data Principal Rights Management cover consent and data principal requests.
The AI Compliance Co-pilot ties it together, and the full set is on the solutions page.
Questions Worth Asking Now
Seven months out, six questions show whether a DPDPA compliance programme is on schedule:
- For one named data principal, where does their data sit, and in how many systems?
- Do those systems agree on who that person is?
- If you run a group, who owns DPDPA compliance at group level, and who owns it at each entity?
- Which regulators govern which of your entities, and has anyone mapped where their requirements overlap?
- Has discovery started, and how early?
- Can your vendor explain how its platform resolves identity across systems?
If you can answer all six today, you're ahead. If you can't, start with the first one. Privy's DPDP readiness assessment is a place to start.
What Comes Next
IDfy will publish a detailed breakdown of what the first 50 Privy by IDfy implementations have taught us. It will cover the failure patterns that keep showing up across sectors, and the sequencing decisions that separate programmes finishing on schedule from those that stall. [PLACEHOLDER: suggested slug /blog/what-50-implementations-taught-us]
Conclusion
More than 50 Indian enterprises are implementing Privy by IDfy. Once rollouts are complete, the scale reaches 10+ PB of personal data, 500M+ people, and 2B+ consent records (projected). The clock runs to 13 May 2027, whether a programme has started or not. Which of the six questions can you answer today?
See how Privy by IDfy can support your DPDPA compliance programme, book a demo, or write to shivani@idfy.com for a walkthrough.
FAQs
How many Indian enterprises are implementing Privy by IDfy?
More than 50, across banks, insurers, NBFCs, asset management, broking, pension management, fintech and payments, retail, ecommerce and D2C, telecom, real estate and proptech, auto marketplaces, health and wellness, business process services and professional services.
What do the 10+ PB, 500M+, and 2B+ figures mean?
They are projected scale upon full rollout of the ongoing Privy implementations: more than 10 petabytes of personal data discovered and governed, privacy rights protected for more than 500 million people, and more than 2 billion consent records governed in real time.
What does DPDPA compliance involve for an enterprise?
An enterprise needs to meet obligations on notice, consent, security safeguards, breach reporting, and data principal rights. Full substantive DPDPA compliance is due on 13 May 2027, with penalties of up to ₹250 crore per contravention.
What does a Privy by IDfy implementation cover?
The full stack: personal data discovery and governance, continuous compliance and risk, and consent lifecycle management, connected by an AI Compliance Co-pilot. That's 3 pillars and 10 modules, implemented as a full suite or as individual modules.
What do the 50+ enterprises have in common?
They differ in sector, size, and regulator. They share customers who trust them with personal data, the same 13 May 2027 deadline, and a decision to start with Privy by IDfy while the clock is running.
Where was Privy featured in the press?
Privy was featured in Mint's Mumbai edition on 6 October 2026 with a note to Indian enterprises.
Learn what the cross-border data transfer rules under DPDP in India are and how Privy by IDfy helps in data transfer flow in India and outside the country.
What a DPDP solution must have in 2026: consent governance, DPRM automation, processor oversight, RoPA, security, and audit readiness
In this blog we will discuss the several reasons that can lead to DPDP fines and how to avoid the DPDP penalties.